
Why Do We Need Layer-1 Encryption?
1. Fiber Tapping Is a Real Threat
Advanced tapping techniques allow attackers to intercept data by bending or micro-cutting fiber, extracting part of the optical signal without disrupting service. Such attacks are nearly impossible to detect without monitoring.
2. Compliance and Regulatory Pressure
Industries such as finance, government, defense, and healthcare face strict regulations requiring encryption of sensitive data in transit. In many cases, Layer-1 encryption is the only method that meets these compliance requirements while maintaining high-performance connectivity.
3. Inherent Weakness of Higher-Layer Encryption
Higher-layer encryption (VPNs, TLS, IPsec) protects traffic only at specific layers, leaving other parts exposed. It also adds computational overhead, reduces throughput, and introduces latency. Layer-1 encryption avoids these drawbacks by protecting all data without exception.
Core Security Benefits of Layer-1 Optical Encryption
Confidentiality
All data is encrypted at the physical layer, ensuring that unauthorized parties cannot interpret information, even if fiber is tapped.
Data Integrity
Layer-1 encryption ensures the information received is identical to what was sent. If tampering occurs, the system immediately detects it and raises an alert.
Authentication
Both ends of the link validate each other’s identity, ensuring data is only shared between trusted, authorized entities.
Transparency & Performance
Encryption is fully transparent to the applications and services running over the network. It does not reduce bandwidth, alter protocols, or introduce measurable delay, ensuring low-latency, line-rate encryption for bandwidths up to 400G and beyond.
Standards and Compliance
For encryption to be trusted, it must meet internationally recognized standards. Modern Layer-1 optical encryption solutions comply with certifications such as:
- NIST FIPS 140-3 – Federal Information Processing Standard for cryptographic modules.
- Common Criteria EAL2 – Evaluation Assurance Level certification for IT security.
- CNSA (Commercial National Security Algorithm) Suite B 2015 – U.S. government-approved algorithms for protecting classified information.
These standards make Layer-1 encryption suitable for Top Secret communications, regulated financial data, and critical infrastructure traffic.
How is Layer-1 Encryption Implemented?
Encryption at Layer-1 is typically integrated into DWDM transponders, muxponders, or standalone optical encryption platforms.
Key aspects include:
- Algorithm: GCM-AES-256 (Advanced Encryption Standard with 256-bit keys in Galois/Counter Mode), providing high security with efficiency.
- Supported Services: 1GbE to 800GbE Ethernet, Fibre Channel, and other protocols.
- Key Exchange: Encryption keys must be securely exchanged between endpoints. Layer-1 solutions use robust cryptographic key exchange protocols to prevent interception.
- Monitoring: Continuous fiber monitoring detects abnormal attenuation changes, often the first indicator of a tapping attempt.
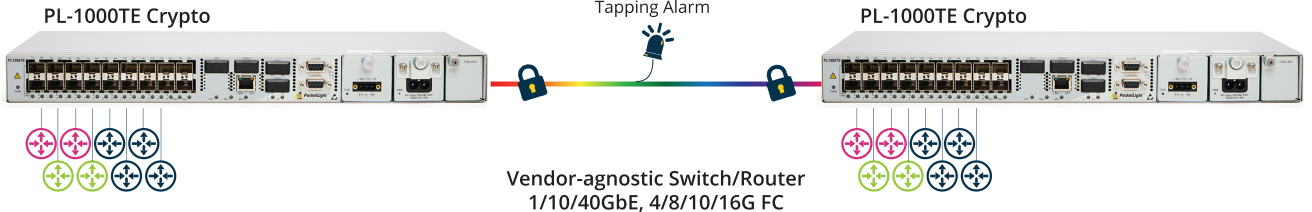
For example, a secure dark fiber link between two data centers can be encrypted at Layer-1, ensuring all traffic, whether backups, real-time applications, or video, is automatically secured without additional encryption layers.
Use Cases of Layer-1 Optical Encryption
- Financial Institutions: Real-time trading requires ultra-low latency. Layer-1 encryption provides security without slowing transactions.
- Government & Defense: Protects classified communications and ensures compliance with national security standards.
- Healthcare: Secures sensitive patient data moving between hospitals, data centers, and cloud environments.
- Cloud & Data Centers: Provides secure, high-bandwidth interconnects for replication, disaster recovery, and tenant isolation.
- Critical Infrastructure: Utilities and transportation networks use Layer-1 encryption to prevent sabotage or espionage.
FAQs About Layer-1 Optical Encryption
What is Layer-1 optical encryption, in simple terms?
It’s a way to encrypt data at the physical fiber layer, ensuring everything transmitted over the fiber is protected—without reducing speed or bandwidth.
How is Layer-1 encryption different from VPN or IPsec encryption?
VPN and IPsec protect specific sessions or protocols and add computational overhead. Layer-1 encryption secures all traffic at line rate, with no added latency or performance loss.
What algorithms are used for Layer-1 encryption?
The most widely adopted standard is AES-256 in Galois/Counter Mode (GCM-AES-256), which provides both strong encryption and integrity verification.
Does Layer-1 encryption affect bandwidth?
No. Since encryption is applied at the optical transport layer, it is fully transparent and preserves the full capacity of the network—whether 10G, 100G, or 400G links.
How does Layer-1 encryption detect fiber tapping?
Solutions continuously monitor the fiber link. If there’s unusual attenuation (loss of signal strength), it may indicate a physical intrusion or tapping attempt, and an alert is triggered.
Who should use Layer-1 encryption?
- Banks and financial institutions that handle high-value, real-time transactions.
- Governments and defense agencies requiring classified communications security.
- Enterprises and cloud providers that must comply with strict data protection regulations.
- Healthcare organizations protecting sensitive medical information.
Is Layer-1 encryption future-proof?
Yes. Modern platforms scale with network demands, supporting current speeds (1G to 400G) and roadmap upgrades to 800G. As new standards and threats emerge, encryption modules can often be updated via firmware or hardware refresh.
Can Layer-1 encryption work in multi-vendor environments?
Yes. Leading solutions, including PacketLight’s, are vendor-neutral and integrate into existing DWDM or dark fiber infrastructures without requiring a complete vendor lock-in.
Does Layer-1 encryption meet compliance regulations like GDPR or HIPAA?
Yes. By protecting data in transit with FIPS- and Common Criteria-certified solutions, organizations can demonstrate compliance with data protection regulations such as GDPR (Europe), HIPAA (healthcare in the U.S.), and various financial security mandates.